

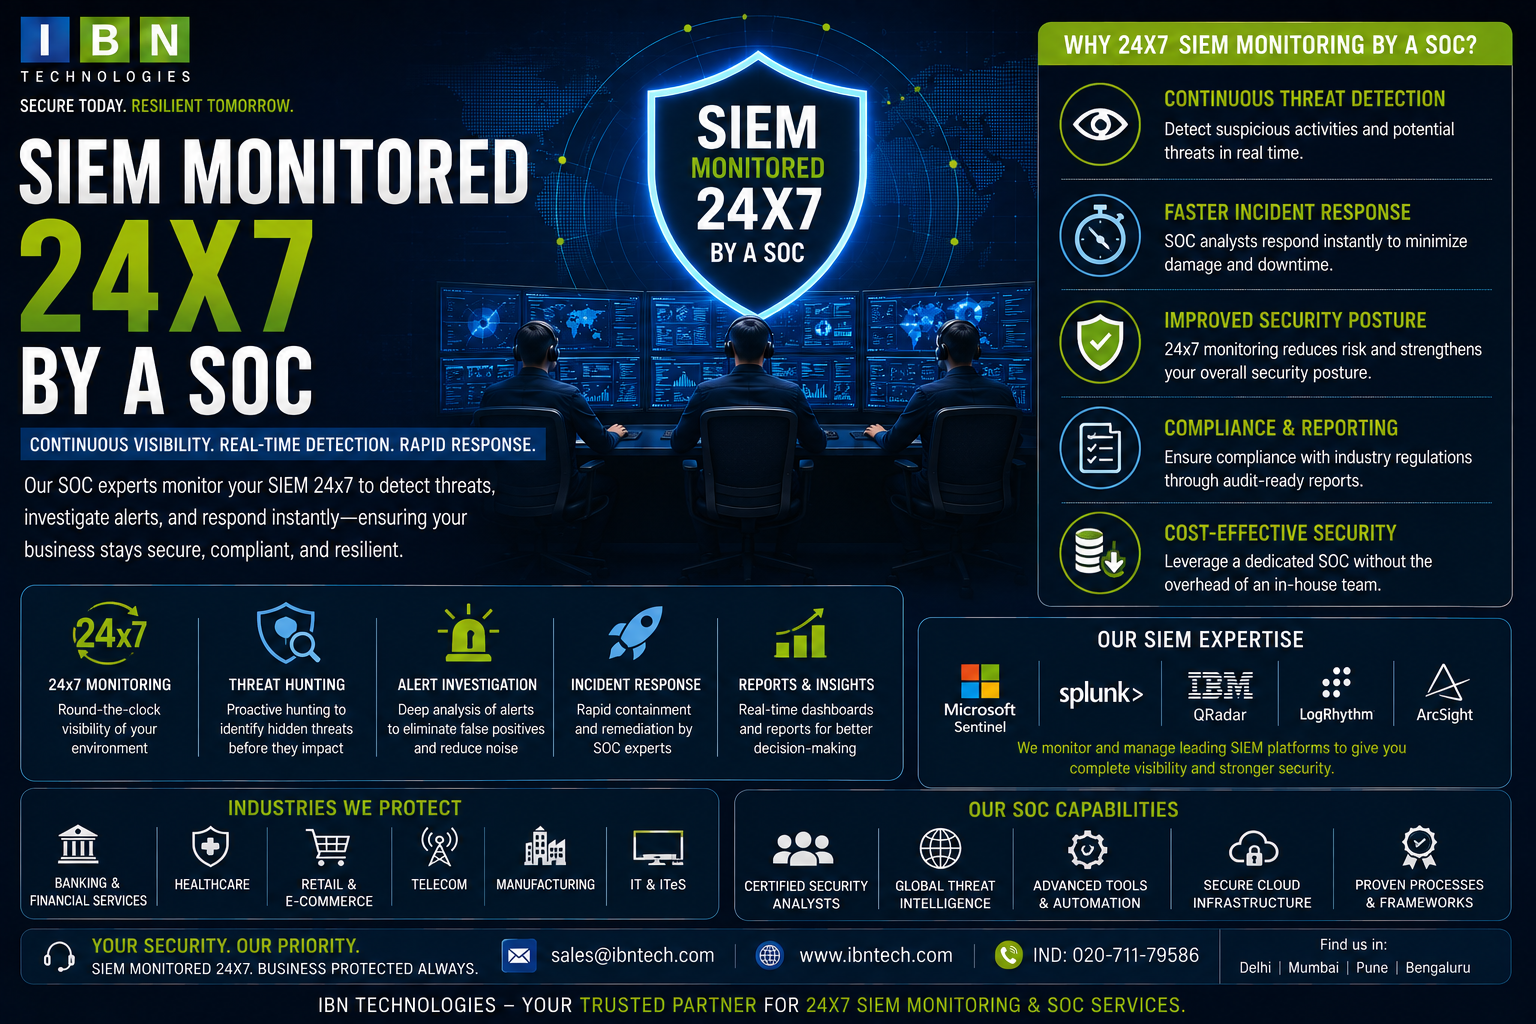
Building Audit-Ready Security Operations With SIEM Monitored 24x7 by a SOC
For ICT organizations, security monitoring is closely connected with operational accountability. Networks, applications, cloud environments, endpoints, and identity systems can produce substantial security information, but collecting logs alone does not demonstrate that security events are being meaningfully reviewed. siem monitored 24x7 by a soc creates a model in which centralized security information can be continuously observed, investigated, and escalated by a security operations team.
This becomes particularly useful when organizations need to demonstrate that security monitoring is part of an established operational process rather than an occasional technical exercise.
What SIEM Monitored 24x7 by a SOC Actually Provides
SIEM monitored 24x7 by a SOC combines centralized security event management with continuous analyst oversight. The SIEM helps organize and correlate relevant security information, while SOC personnel assess alerts and investigate activity that may require attention.
The result is a security operation built around three connected activities: visibility, investigation, and response coordination.
For ICT organizations, this structure can support security governance by creating a more consistent approach to monitoring and documenting relevant security activity.
Why Managed SOC Providers With Compliance Reporting Matter
managed soc providers with compliance reporting can help organizations connect security monitoring with their wider governance requirements. Reporting can provide stakeholders with information about monitored environments, security events, investigations, and relevant operational activity.
The exact reporting scope should be established according to the organization's needs and applicable requirements.
Compliance reporting should not be treated as a collection of generic documents. Useful reporting should help an organization understand what was monitored, which events required investigation, how incidents were handled, and where security operations may need improvement.
For ICT businesses, this can make security monitoring more transparent to both technical and management stakeholders.
Security Visibility Is Not the Same as Compliance
Organizations sometimes assume that deploying a SIEM automatically creates a compliant security-monitoring program.
In practice, technology is only one component.
A meaningful monitoring framework also needs defined responsibilities, appropriate data sources, alert-handling procedures, escalation rules, incident records, and management oversight.
A SIEM may retain security events, but organizations still need processes that determine how those events are reviewed and what happens when suspicious activity is identified.
A managed SOC can provide the operational layer needed to connect security data with analyst-led investigation and reporting.
How SIEM Monitoring Can Support Security Governance
The process begins with identifying the systems and security information relevant to the organization's security objectives.
Events are then collected into the monitoring environment. Detection rules and other mechanisms can highlight potentially suspicious activity.
SOC analysts review relevant alerts, investigate available context, and determine whether further escalation is appropriate.
The investigation and escalation process can produce operational information that supports security reporting. Depending on the service arrangement, reports may help management understand security activity, monitoring coverage, significant events, and incident-handling processes.
This creates a connection between technical monitoring and governance oversight.
Why Manual Security Reviews Can Fall Short
ICT environments rarely remain static. New systems, applications, users, cloud services, and network components can alter the organization's security landscape.
A manual approach can make it difficult to maintain consistent monitoring as the environment expands.
Internal staff may also have competing operational responsibilities. Reviewing security events manually after routine IT tasks are completed can create inconsistent coverage.
A dedicated SOC provides a defined operational function for monitoring and investigation.
This does not mean every event requires immediate human intervention. Effective SOC operations depend on detection logic and prioritization so that analysts can focus attention where it is most useful.
What a Strong Compliance-Oriented SOC Should Cover
An ICT organization assessing a managed SOC should look beyond the phrase "compliance reporting."
Key areas include:
- Clear monitoring scope.
- Defined security data sources.
- Documented alert-handling procedures.
- Investigation workflows.
- Incident escalation criteria.
- Security event documentation.
- Reporting appropriate for technical teams.
- Management-level reporting where required.
- Defined incident ownership.
- Clear responsibilities for remediation.
- Processes for adding new technology to monitoring.
- Regular review of monitoring coverage.
- Appropriate retention and access practices for security information.
- Periodic assessment of service performance.
The objective is to establish an evidence-based security operation that supports organizational oversight.
An ICT Example: Preparing for a Security Review
Consider an ICT company preparing for an internal security review.
The organization already has security tools deployed, but security stakeholders need to understand whether alerts are consistently reviewed and investigated.
A 24x7 SOC model can provide a structured process for monitoring relevant security events. When suspicious activity is detected, analysts investigate it and document the outcome according to the operating model.
Management can then receive appropriate reporting about monitoring activity and significant security events.
This does not guarantee compliance with every requirement. Instead, it creates a stronger operational foundation from which the organization can demonstrate how security monitoring is performed.
Reporting Should Serve Decision-Makers
Security reports are most useful when they answer practical questions.
Technical teams may want to understand significant alerts, investigation activity, monitoring gaps, or changes in security patterns.
Management may be more interested in the overall state of security operations, notable incidents, unresolved issues, and areas requiring attention.
A good reporting model should therefore distinguish between operational detail and management-level information.
Reports should also avoid overwhelming stakeholders with data that does not support a decision. More pages do not necessarily mean better security governance.
Selecting a Provider for Compliance-Focused Monitoring
ICT organizations should ask prospective providers how reporting fits into their SOC operation.
They should understand:
- What security events are monitored.
- How alerts are investigated.
- What constitutes an escalation.
- How investigations are documented.
- What reports are available.
- How often reporting is delivered.
- Which stakeholders receive reports.
- How significant incidents are communicated.
- How monitoring coverage is reviewed.
- How changes in the technology environment are incorporated.
- Which compliance-oriented activities are included in the service.
- Which responsibilities remain with the customer.
This evaluation helps separate genuine operational support from a service that simply provides periodic security summaries.
Governance and Compliance Responsibilities
Security monitoring can support governance, but organizations remain responsible for understanding and meeting the requirements applicable to their operations.
A managed SOC may assist with monitoring, investigation, reporting, incident handling, and other security activities within the agreed scope.
The organization should still maintain ownership of its security policies, risk decisions, access governance, incident authority, and applicable regulatory responsibilities.
For ICT leaders, this distinction is important. A provider can supply operational evidence and security expertise, but organizational governance cannot be delegated without appropriate oversight.
Turning Monitoring Into Demonstrable Security Practice
A strong security program should be capable of answering not only "Are we collecting security data?" but also "Who reviews it, what happens when something looks suspicious, and how is that activity documented?"
For Indian ICT organizations, siem monitored 24x7 by a soc provides a framework for connecting continuous monitoring with analyst investigation and security reporting.
When paired with appropriate managed soc providers with compliance reporting, organizations can create a clearer operational record of monitoring activity, investigations, escalations, and security events.
The strongest approach is not to treat reporting as an end-of-process administrative task. It should be connected directly to the monitoring operation so that security information becomes useful evidence for technical teams, management, and governance stakeholders.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - sales@ibntech.com


