

Building Stronger IT Security Through Structured SOC Audits
Modern IT organizations manage complex digital environments that include cloud platforms, enterprise applications, remote access systems, and customer-facing technologies. While digital transformation improves business efficiency, it also increases cybersecurity responsibilities.
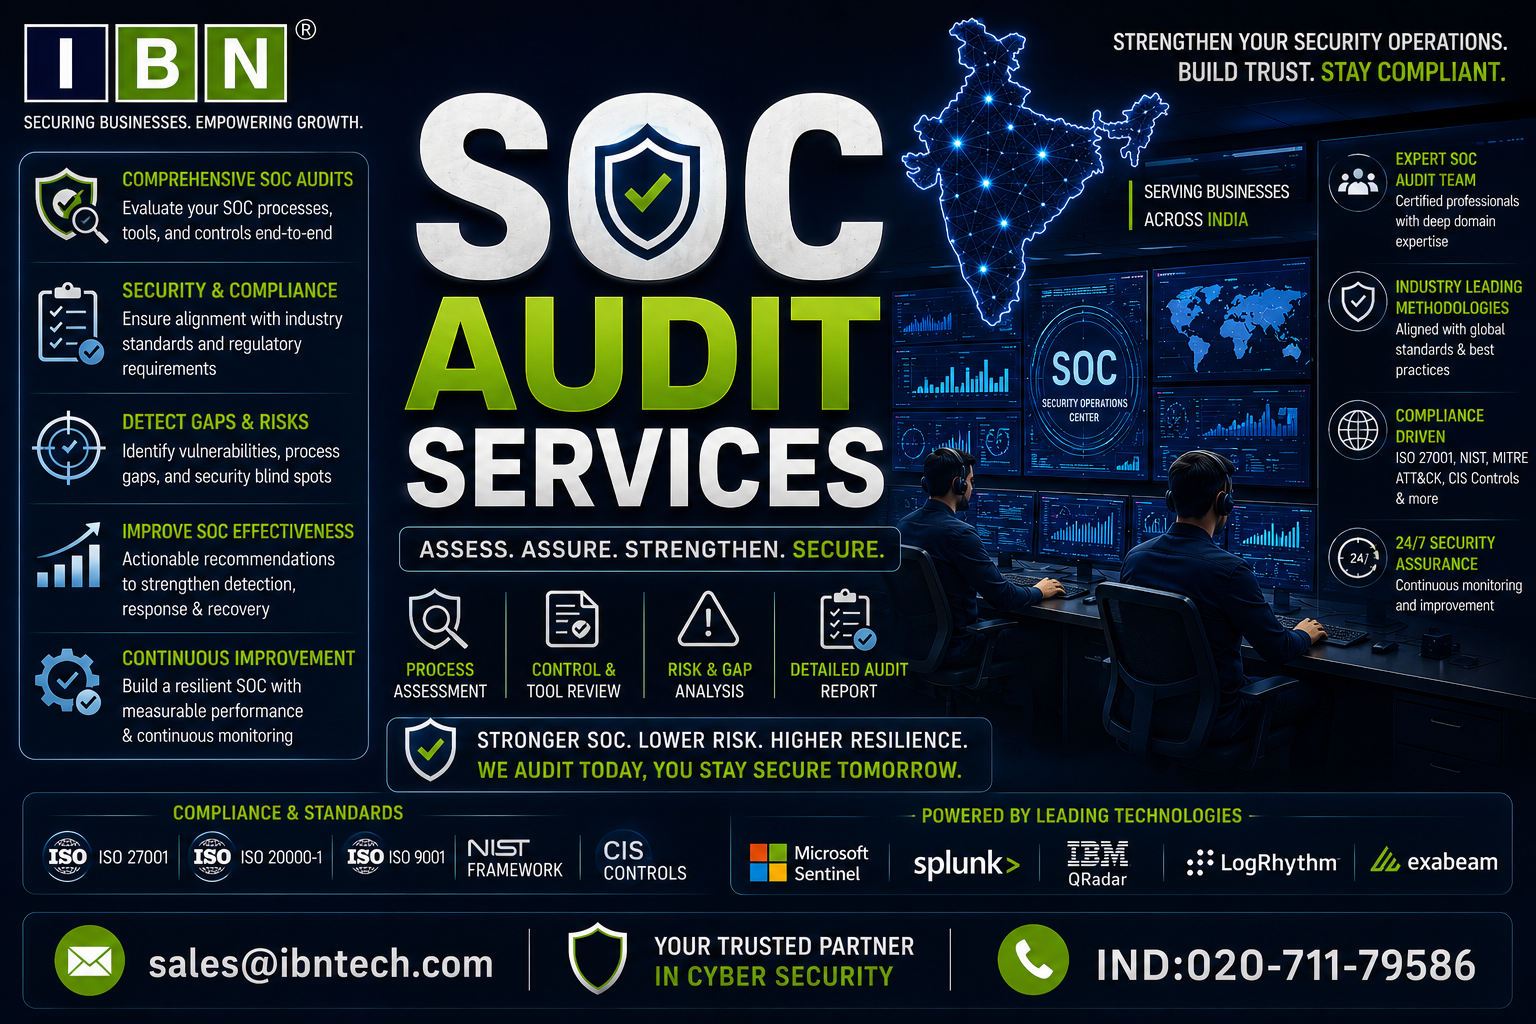
Companies looking for soc audit services want to understand whether their Security Operations Center processes, monitoring capabilities, and incident response practices are working effectively. A structured SOC Security Assessment helps organizations identify security gaps, improve operational visibility, and build a stronger cybersecurity framework.
A SOC audit is not only a technical review. It is an evaluation of how effectively an organization detects, investigates, and responds to cybersecurity events.
Why SOC Audit Services India Matter for IT Organizations
IT companies often manage critical applications, infrastructure, and customer data. Any weakness in security monitoring can create risks that affect business continuity, service delivery, and customer confidence.
A SOC audit helps organizations review important areas such as:
- Security monitoring processes
- Alert management practices
- Incident response procedures
- Security visibility across systems
- Operational workflows
- Existing security controls
For IT leaders, understanding these areas helps improve decision-making and ensures cybersecurity investments deliver better value.
The Growing Need for SOC Security Assessment
Cyber threats continue to evolve as businesses adopt new technologies. IT environments now include multiple platforms, applications, and access points that generate large amounts of security information.
Common challenges include:
- Increasing security alerts
- Limited visibility across environments
- Difficulty prioritizing incidents
- Inconsistent monitoring processes
- Lack of structured response procedures
A SOC Security Assessment provides organizations with a clearer understanding of their current security operations and areas requiring improvement.
Why Traditional Security Reviews Are Not Enough
Many organizations perform periodic security checks focused on individual systems or tools. While these reviews provide useful information, they may not provide a complete view of SOC effectiveness.
A SOC audit evaluates the overall security operation, including people, processes, and technology.
|
Traditional Security Review |
SOC Audit Approach |
|
Focuses on individual controls |
Reviews complete security operations |
|
Limited operational visibility |
Evaluates monitoring effectiveness |
|
Tool-focused analysis |
Process and technology assessment |
|
Periodic review activity |
Continuous improvement approach |
This broader perspective helps IT organizations improve security maturity.
How SOC Audits Work for IT Businesses
A SOC audit typically evaluates multiple components of security operations.
Reviewing Security Monitoring Capabilities
The assessment examines how security events are collected, monitored, and analyzed across different technology environments.
Evaluating Alert Management
Auditors review how alerts are categorized, prioritized, and handled by security teams.
Assessing Incident Response
The process evaluates whether response procedures are clearly defined and effective during cybersecurity incidents.
Identifying Improvement Opportunities
Findings from the assessment help organizations strengthen processes and improve security operations.
This structured approach enables IT companies to move toward proactive cybersecurity management.
Benefits of SOC Audit Services for IT Organizations
A well-executed SOC audit provides several business advantages.
Organizations can achieve:
- Better understanding of security strengths and weaknesses
- Improved incident response readiness
- Enhanced security monitoring processes
- Stronger operational visibility
- More effective use of security resources
- Improved cybersecurity governance
For IT companies serving enterprise customers, demonstrating strong security practices can also improve customer confidence.
IT Industry Use Case
An IT services company manages cloud infrastructure and business applications for multiple customers. The organization has implemented several security technologies but wants to evaluate whether its monitoring processes are effective.
Internal teams notice challenges in managing security alerts and maintaining consistent incident response procedures.
Through a SOC Security Assessment, the company reviews its monitoring workflows, alert handling process, and response approach. The assessment identifies opportunities to improve visibility and create more structured security operations.
As a result, the organization gains better control over cybersecurity processes while supporting future business expansion.
Key Areas to Review During a SOC Audit
IT leaders should evaluate several important areas when conducting a SOC audit.
|
Audit Area |
Purpose |
|
Monitoring processes |
Understand security visibility |
|
Alert handling |
Improve incident prioritization |
|
Response procedures |
Strengthen incident management |
|
Security reporting |
Improve decision-making |
|
Technology integration |
Ensure effective monitoring |
A detailed evaluation helps organizations create a more mature security operation.
Compliance and Governance Considerations
IT organizations often work with customers that require strong security practices and responsible data protection measures.
SOC audits support governance by helping businesses review security processes, improve documentation, and maintain better visibility into cybersecurity operations.
Regular security assessments also help organizations identify improvement areas before they become operational challenges.
Improving IT Security Through Continuous Evaluation
Cybersecurity is not a one-time activity. As technology environments evolve, organizations need regular assessments to ensure security operations remain effective.
Implementing soc audit services enables IT companies to evaluate their security operations, strengthen monitoring practices, and improve cyber resilience through a structured SOC Security Assessment approach.


